Planet Drupal

Security and Drupal Presentation Slides from Drupalcon DC

Friday morning at Drupalcon DC, Matt Cheney, Neil Drumm, Ezra B. Gildesgame and I gave two presentations about keeping Drupal sites secure: Introduction to Security and Advanced Drupal Security.

Crying Wolf? Second Security Advisory for 2009 is a Public Service Announcement

The second security advisory for Drupal core in 2009 was just released - SA-CORE-2009-002 Drupal core - Administer content types permission. It is a "public service announcement" reminding site admins that "administer content types" is a very broad permission which, in the hands of a malicious user, includes the ability to take over a site (Edit: on many sites...not all.).

For most sites this doesn't require any action. So, why post the SA at all?

Disclosures Made Outside Security Process

Update UID1 Password Via Javascript - Ported to Drupal 6.x

Heine Deelstra created a script to update UID 1 password via JavaScript. This script needed some updating to work with Drupal 6.x and since my book - Cracking Drupal is primarily about Drupal 6.x I updated the script. You will find the script attached and presented below:

// Test for  the presence of jquery.
if (typeof jQuery == 'function') {

Drupal Core Point Releases - Too Often? Too Few? Just Right?

In general, Drupal core releases are created whenever there is a major security issue.

What is the Drupal Core Release Process?

The process goes something like this:

  1. Vulnerability is identified (internally or externally) and the security team learns of it
  2. Depending on the severity of the issue and the complexity of fixing it, people set about to fix it
  3. repeat steps 1 and 2 until there is a critical mass of issues that make it worthwhile to create a release. An exploit in the wild (if that ever were to happen) also triggers a release

What Kinds of Security Problems Exist in Drupal?

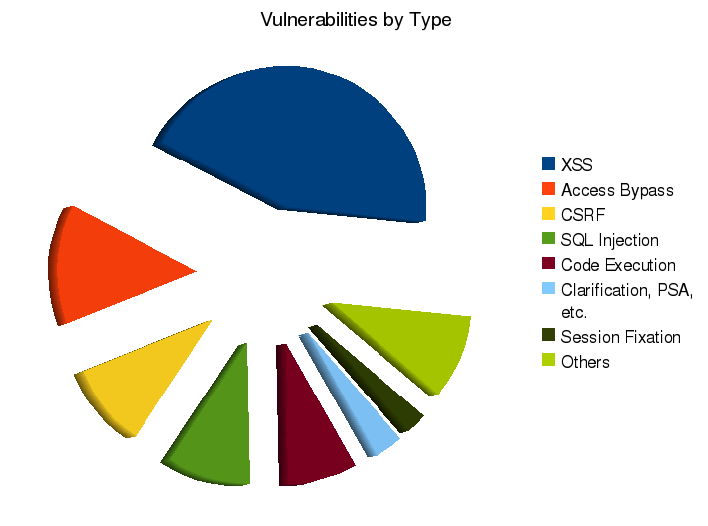
As part of writing the book I did some analysis looking at all of the security announcements in the history of the Drupal project.

This pie chart shows which are the most common kinds of problems in the project:

security weaknesses in Drupal

Vulnerable Module - A Demonstration of Horrible Drupal Programming Practices

This is possibly the worst Drupal module. Ever. You should only install it on test sites which are not publicly accessible such as a test server inside a company firewall or your own laptop (behind its own firewall). You can also learn from it simply by reading the code.

Syndicate content